For years, managed IT services meant one thing: keeping the lights on. Servers running, networks connected, help desk tickets resolved. That was the job, and for a while, it was enough. But the technology landscape has shifted, and so have the risks that come with it. Today, treating IT management and cybersecurity as separate functions isn’t just outdated—it’s dangerous.
Businesses that still view their managed service provider purely as a maintenance crew are missing a critical piece of the puzzle. Uptime and functionality mean little if a single unpatched vulnerability can bring an entire operation to a halt. That’s why the smartest organizations are rethinking what they expect from their IT partners.
The Old Model Wasn’t Built for Today’s Threats
Traditional managed IT services grew out of a need for efficiency. Businesses wanted reliable systems without the overhead of a full internal IT department, so providers stepped in to monitor networks, update software, and troubleshoot problems as they arose. Security, when it existed, was often an afterthought—a basic firewall or antivirus program bolted onto the service package.
That approach made sense in a simpler digital environment. But cyber threats have grown more sophisticated, more frequent, and more costly to ignore. Attackers no longer need to breach a fortress; they just need one overlooked gap. A siloed approach to IT and security creates exactly those gaps, leaving businesses exposed even when their systems appear to be running smoothly on the surface.
What Integration Actually Looks Like
Integrated cybersecurity isn’t about adding a few extra tools to an existing IT stack. It’s about building security into the foundation of how systems are managed, monitored, and maintained. This means threat detection isn’t a separate service running parallel to IT operations—it’s woven into daily monitoring. Patch management isn’t just about keeping software current; it’s about closing vulnerabilities before they can be exploited.
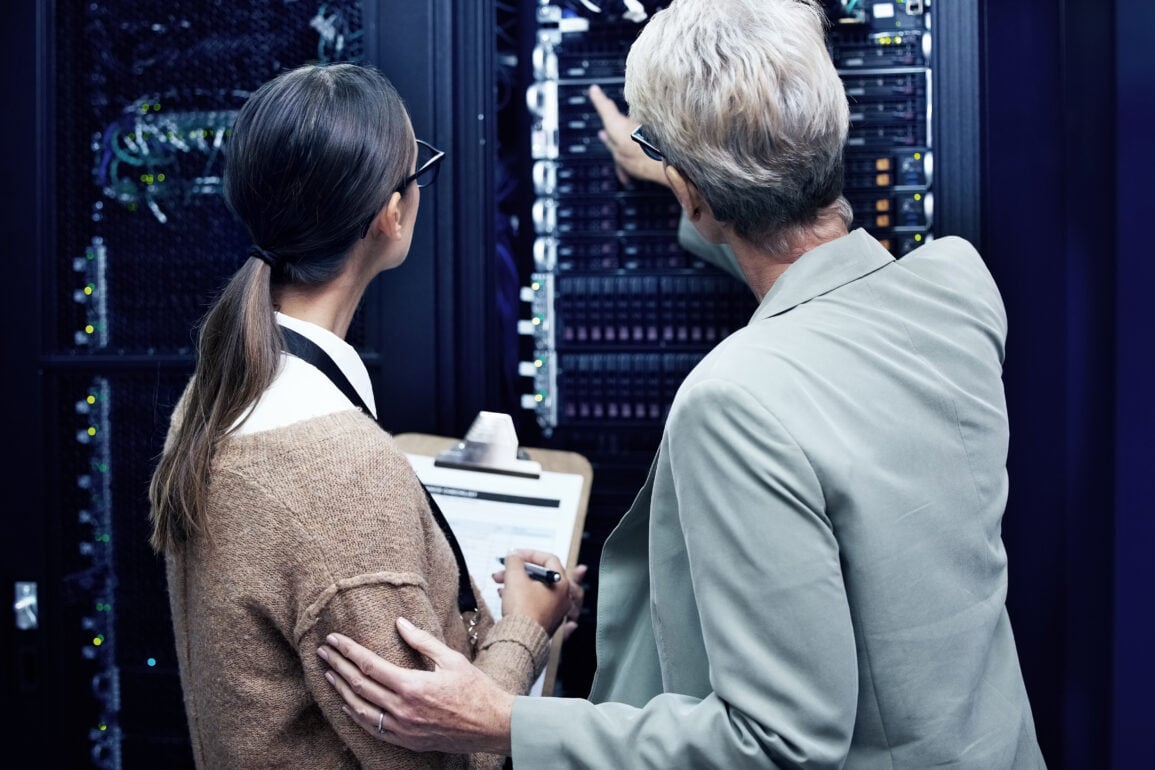
This kind of integration also changes how problems get solved. When IT and security teams operate independently, response times suffer. Something is a network problem, then a fingers get pointed while a security issue slips through. With integrated services, there’s a single point of accountability and a unified view of what’s happening across the entire environment. Issues get identified faster because the people managing the network are the same people watching for threats.
The Business Case for a Unified Approach
Beyond the technical advantages, there’s a practical business argument for integration. Managing separate vendors for IT support and cybersecurity creates friction. Contracts overlap, responsibilities blur, and when something goes wrong, businesses often find themselves caught between providers who each claim the issue falls outside their scope.
A unified approach eliminates that ambiguity. It also tends to be more cost-effective, since businesses aren’t paying for redundant monitoring tools or duplicated administrative overhead. More importantly, it allows for better strategic planning. When one partner understands both the operational and security needs of a business, they can make smarter recommendations about where to invest in technology upgrades, staff training, or policy changes.
There’s also the matter of compliance. Industries with strict regulatory requirements around data protection can’t afford to treat security as an add-on. Integrated managed services make it easier to maintain consistent documentation, enforce policies uniformly, and respond quickly when audits or incidents demand a clear paper trail.
Preparing for What’s Next
Cyber threats aren’t going to become less sophisticated, and the businesses that thrive will be the ones that stop treating security as optional. This doesn’t mean every organization needs an in-house security operations center or a massive technology overhaul. It means choosing an IT partner who understands that management and protection go hand in hand.
The conversation with any current or prospective provider should start with a simple question: how is security built into your service, not bolted onto it? The answer will reveal a lot about whether that partnership is equipped to handle what’s ahead.
Managed IT services will always be about keeping systems running. But in a landscape where threats evolve daily, that’s no longer the whole story. Integrated cybersecurity isn’t an upgrade to managed services—it’s what makes them complete.